CeFPro Connect

Connect Plus Ad

Video

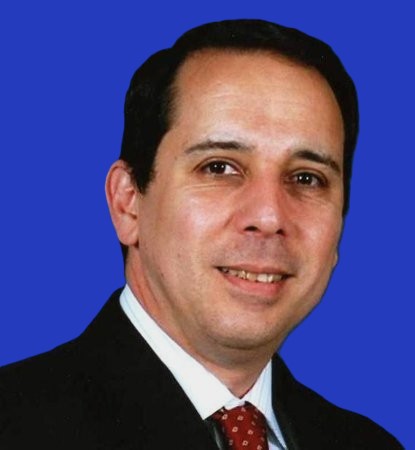
Francesco De Lucia Dattolo Calls for a Shift from Risk Reporting to Risk Intelligence
Francesco De Lucia Dattolo, TPRM Program Manager at Schlumberger, explains why third-party risk management must evolve beyond vendor ratings to deliver actionable business intelligence. He highlights the growing importance of predictive risk insights, business-focused communication, and decision-making that strengthens organizational resilience.
Oct 30, 2026
Francesco De Lucia Dattolo
Francesco De Lucia Dattolo, TPRM Program Manager, Schlumberger (SLB)
Tags: Vendor and Third Party Risk
The views and opinions expressed in this content are those of the thought leader as an individual and are not attributed to CeFPro or any other organization

Francesco De Lucia Dattolo, TPRM Program Manager at Schlumberger, shares his perspective on why traditional third-party risk reporting often fails to provide value to business leaders. He explains that risk professionals should translate technical findings into meaningful business outcomes, focusing on operational, financial, and reputational impacts rather than vendor ratings alone.


During the interview, Dattolo discusses the growing need for predictive risk intelligence, executive-focused communication, and a deeper understanding of business context. He argues that organizations must evolve from measuring risk through scores and assessments to delivering insights that improve decision-making, increase resilience, and help businesses anticipate future challenges.

Francesco De Lucia Dattolo Bio

Francesco De Lucia is a seasoned cybersecurity and technology program leader with more than 25 years of experience driving enterprise governance, risk management, and digital supply chain resilience across global organizations. He specializes in transforming complex compliance expectations into practical, scalable controls embedded throughout procurement, third party risk, and cross functional operational processes. Known for his ability to bridge executive strategy with real world execution, Francesco builds programs that strengthen supplier resilience, elevate cyber maturity, and deliver sustainable security outcomes at scale. His work centers on aligning organizations to frameworks such as NIST CSF while ensuring that governance models remain adaptable, efficient, and globally consistent. Francesco is recognized for advancing enterprise security through disciplined leadership, clear operational design, and a pragmatic approach that turns cyber risk management into a measurable business enabler.

Francesco De Lucia Dattolo
Sign in to view comments
You may also like...
Related insights —
Connect Plus Ad