Join a community of professionals and get:
on all CeFPro events.
unlock speaker decks and audience polls.
Full library access the moment you sign up.
Digital Content

- Unlimited access to peer-contribution articles and insights
- Global research and market intelligence reports
- Discover Connect Magazine, a monthly publication
- Panel discussion and presentation recordings
Webinar


The webinar explores how AI is changing the third-party risk landscape, making risks more interconnected, fast-moving and difficult to assess through traditional, siloed frameworks. As vendors increasingly incorporate AI into their processes, organisations may find that what they assessed at onboarding can change significantly over time, while critical dependencies can sit several layers beyond the contracted third party. The discussion looks at the limitations of point-in-time assessments and the need for more continuous approaches to understanding third-party exposure.
The panel also explores how organisations can respond through integrated risk management, dependency mapping, critical dependency registers, concentration and correlated risk limits, stronger fourth-party governance and early warning indicators. The speakers consider how TPRM, cyber risk and AI risk need to work together to identify cascading and correlated failures, while also discussing how the traditional three lines of defence can evolve to support this changing risk environment.
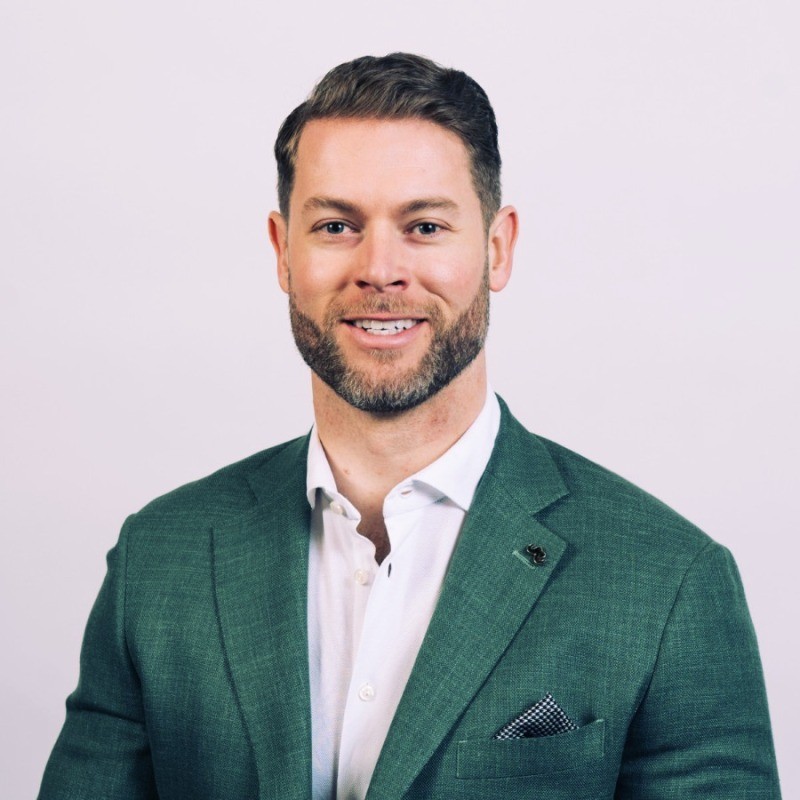
Johnathan focuses on helping customers operationalize cyber risk intelligence to drive risk reduction across digital and physical supply chains. Over the past two years, he has had the privilege of working with 300+ enterprise TPRM programs across North America. What has he learned? That TPRM is undergoing a massive industry transformation. He will be sharing the best strategies for strengthening third-party cyber risk management programs—helping organizations shift their perspective to assess vendors the way adversaries do. Johnathan will discuss how to identify vendor ransomware susceptibility, drive vendor engagement at scale, and reinvent cyber assessments with actionable cyber risk intelligence to improve security outcomes.

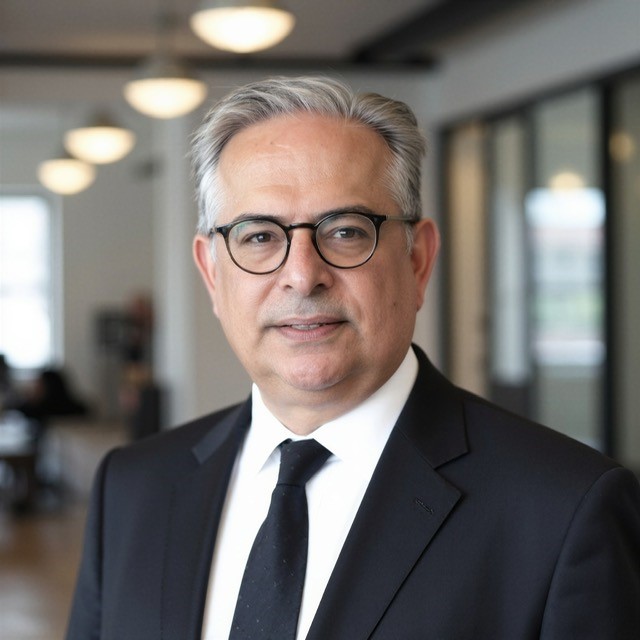
Nabeel Alvie is a seasoned professional with over 30 years of experience in diversified risk management and Internal Audit. He has managed internal control and risk management frameworks for corporate, commercial, investment banking and capital markets products and services for some of the world’s largest and most complex financial institutions. His risk management expertise cover a broad spectrum of financial and non-financial risk strips including operational risk including third-party risk management, credit risk, enterprise risk and market risk On the regulatory front, he has expertise in Basel, CCAR, DFAST, LCR, Heightened Standards, LIBOR Transition and CECL. He has worked in major global financial centers, including the USA, EMEA and Asia-Pacific. He holds a Bachelor’s degree in Business Administration from California State University
Biography coming soon