PREMIUM CONTENT
This is premium content, available to Connect Plus users only
Unlock this content and more with Connect Plus membership.
Join a community of professionals and get:
Join a community of professionals and get:
15% discount
on all CeFPro events.
on all CeFPro events.
Post-event access:
unlock speaker decks and audience polls.
unlock speaker decks and audience polls.
Instant insights:
Full library access the moment you sign up.
Full library access the moment you sign up.
Article
Supplier Diversity Can Hide Dangerous Concentration Risk
Financial institutions may appear to have diversified supplier ecosystems while remaining dangerously dependent on shared underlying infrastructure. Milena Maneva, Head of Business Continuity & Resilience EMEA at Cantor Fitzgerald & BGC Group, argues that effective third-party risk management requires firms to understand and test the dependencies behind their suppliers.
Sep 17, 2026
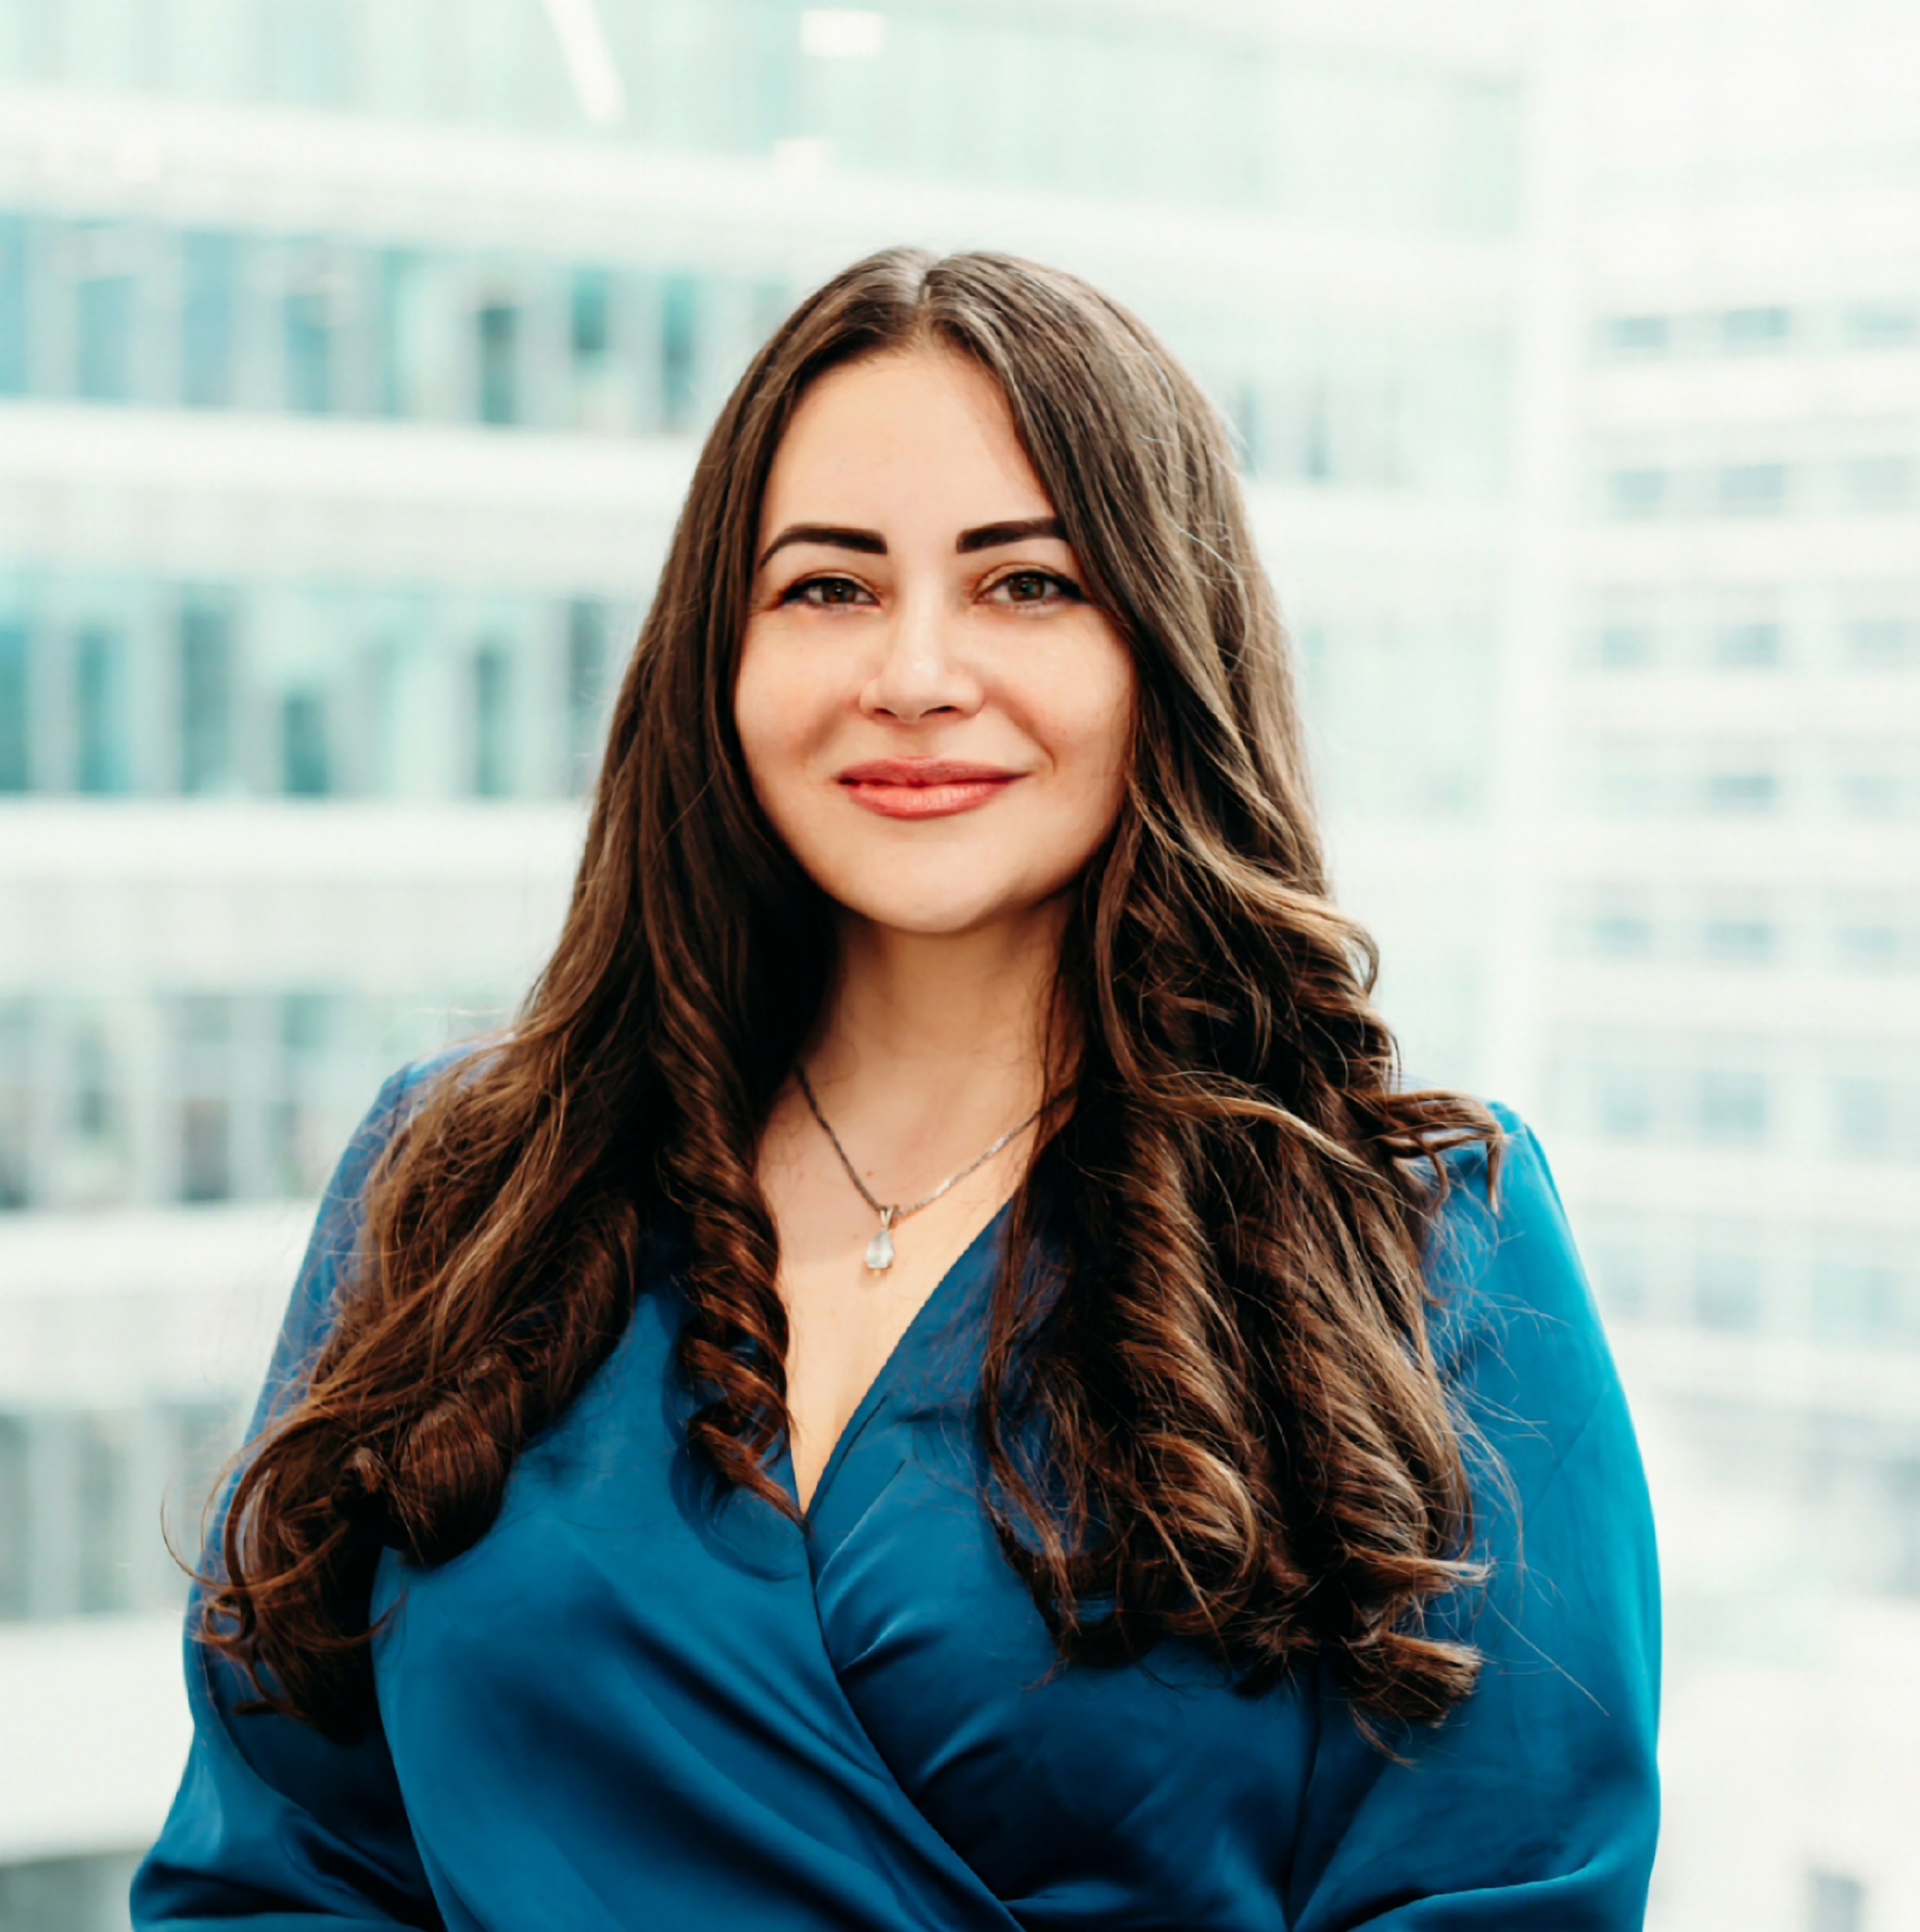
Milena Maneva, Head of Business Continuity & Resilience EMEA, Cantor Fitzgerald & BGC Group
Tags:
Vendor and Third Party Risk
The views and opinions expressed in this content are those of the thought leader as an individual and are not attributed to CeFPro or any other organization
- Business owners
should retain accountability for the risks created by third-party
relationships
- Integrated
assessments should focus on critical services and dependencies rather than
isolated risk disciplines
- Due diligence must
identify fourth parties and hidden infrastructure dependencies
- Critical recovery
plans should be tested rather than simply accepted as assurance
- Supplier
diversification can conceal concentration in shared cloud, technology or
geographic dependencies
- Resilience is
ultimately measured by the ability to continue operating when a critical
supplier fails
Log in to continue or register for free
WHAT'S INCLUDED:
Unlimited access to peer-contribution articles and insights
Global research and market intelligence reports
Discover Connect Magazine, a monthly publication
Panel discussion and presentation recordings
Sign in to view comments
Related insights —