PREMIUM CONTENT
This is premium content, available to Connect Plus users only
Unlock this content and more with Connect Plus membership.
Join a community of professionals and get:
Join a community of professionals and get:
15% discount
on all CeFPro events.
on all CeFPro events.
Post-event access:
unlock speaker decks and audience polls.
unlock speaker decks and audience polls.
Instant insights:
Full library access the moment you sign up.
Full library access the moment you sign up.
Event Q&A
Third-Party Risk in Agentic AI Ecosystems
Naresh Raheja explores how agentic AI is reshaping third-party risk management by introducing dynamic dependencies, complex permission structures, and interconnected service ecosystems that extend far beyond traditional vendor relationships. He discusses practical approaches for mapping fourth-party and nth-party dependencies, examines growing regulatory expectations around AI governance, and outlines how firms can prepare for future concentration and resilience risks associated with increasingly critical AI infrastructures.
Sep 25, 2026
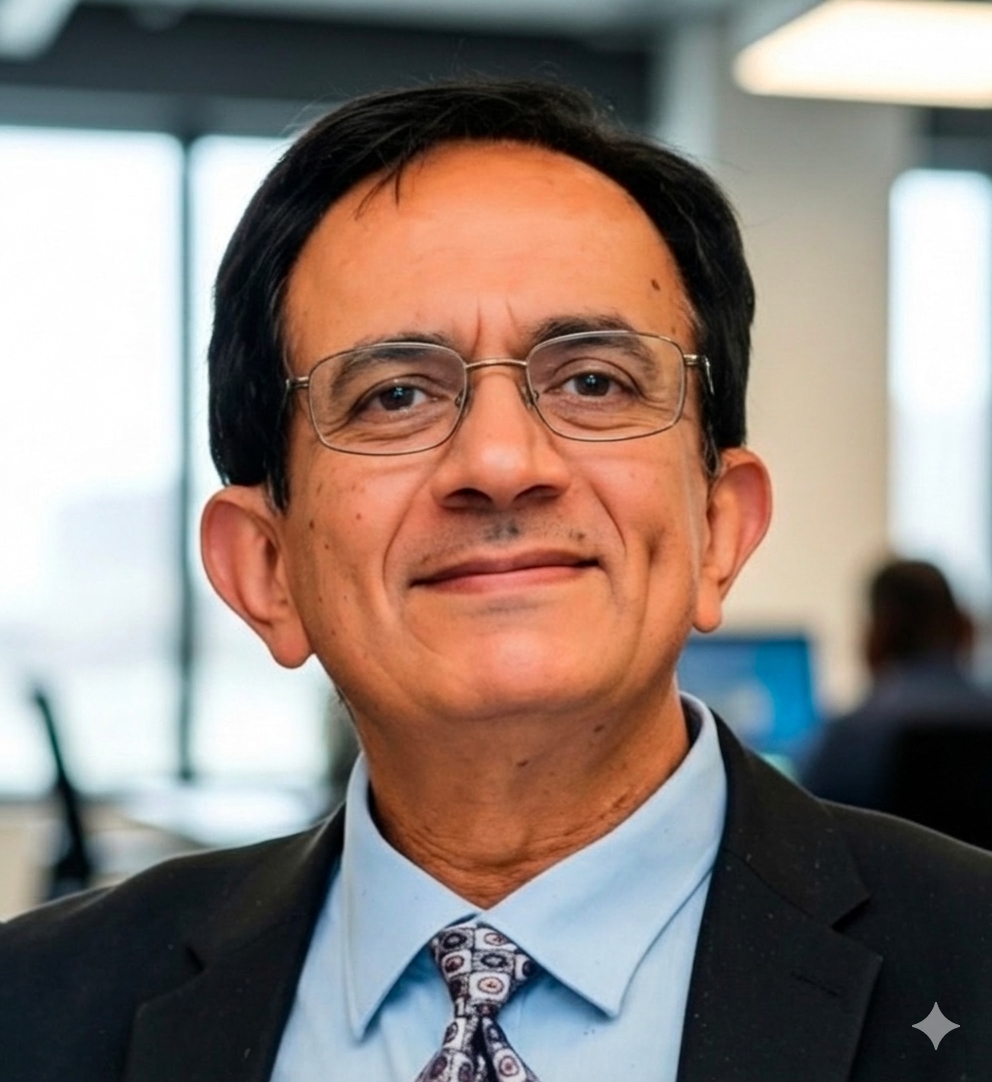
Naresh Raheja, Former OCC - Senior Risk Speciality and Examiner, Independent
Tags:
Vendor and Third Party Risk
The views and opinions expressed in this content are those of the thought leader as an individual and are not attributed to CeFPro or any other organization
- Traditional TPRM frameworks struggle to capture agentic AI pathways, permissions, and dynamic dependencies.
- Visibility into fourth-party and nth-party dependencies remains a major challenge for organizations.
- AI governance requires integration across model risk, TPRM, cyber, resilience, and operational risk functions.
- Existing TPRM frameworks remain relevant but must become more dynamic and event-driven.
- Concentration risk within AI ecosystems may become a systemic challenge similar to cloud dependency risks.
- Organizations should build capabilities around transparency, resilience, substitutability, and continuous monitoring.
Log in to continue or register for free
WHAT'S INCLUDED:
Unlimited access to peer-contribution articles and insights
Global research and market intelligence reports
Discover Connect Magazine, a monthly publication
Panel discussion and presentation recordings
Related insights —