PREMIUM CONTENT
This is premium content, available to Connect Plus users only
Unlock this content and more with Connect Plus membership.
Join a community of professionals and get:
Join a community of professionals and get:
15% discount
on all CeFPro events.
on all CeFPro events.
Post-event access:
unlock speaker decks and audience polls.
unlock speaker decks and audience polls.
Instant insights:
Full library access the moment you sign up.
Full library access the moment you sign up.
Article
Agentic AI Exposes Dangerous Blind Spots in Third Party Risk Management
Agentic AI is creating new vulnerabilities that traditional third-party risk management frameworks may struggle to identify. Former OCC Senior Risk Specialist Naresh Raheja warns that dynamic dependencies, complex permissions and limited supplier transparency threaten operational resilience. He argues that financial institutions must strengthen governance, continuously monitor interconnected AI ecosystems and prepare for emerging concentration risks.
Nov 06, 2026
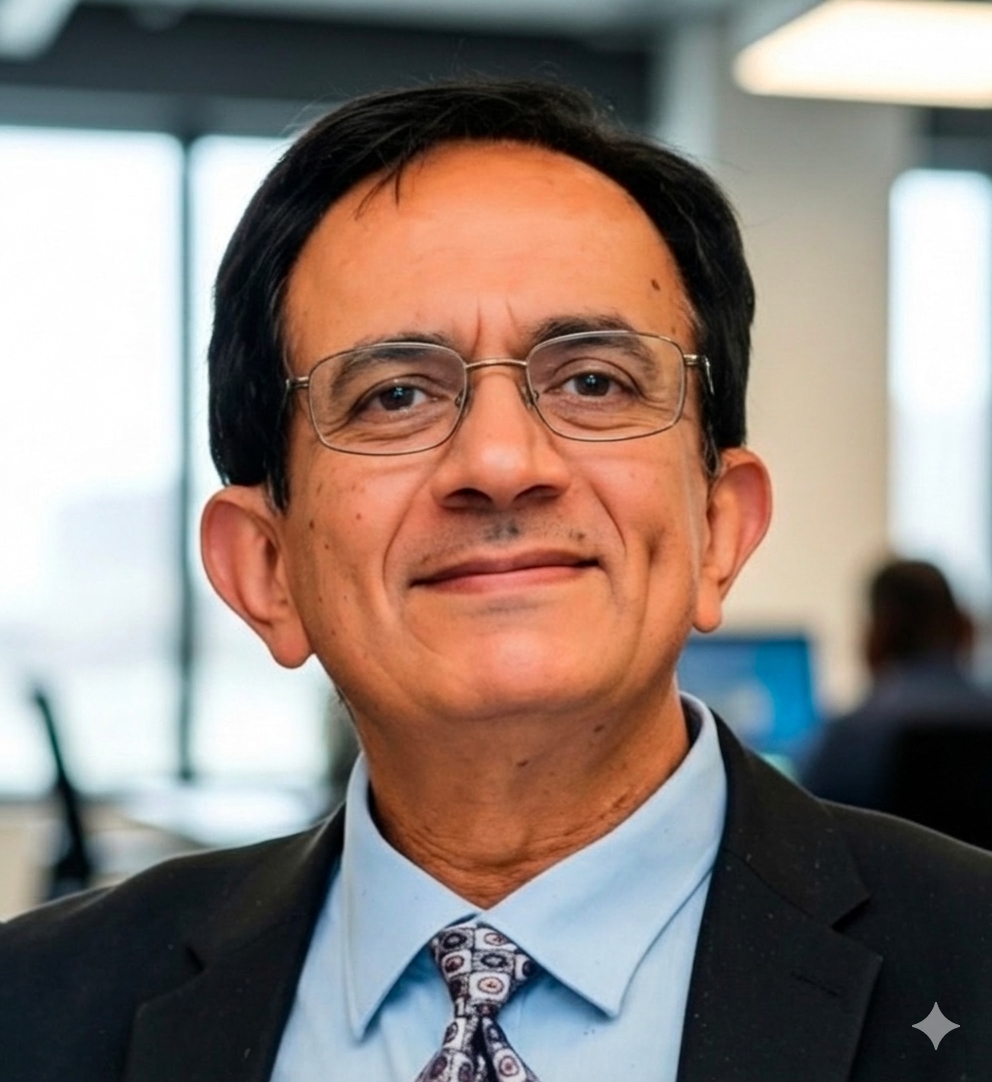
Naresh Raheja, Former OCC - Senior Risk Speciality and Examiner, Independent
Tags:
Vendor and Third Party Risk
The views and opinions expressed in this content are those of the thought leader as an individual and are not attributed to CeFPro or any other organization
- Agentic AI creates
dynamic dependencies that traditional third-party risk frameworks struggle
to capture
- AI pathways,
permissions and system capabilities introduce risks beyond individual
vendor relationships
- Fourth-party
visibility requires continuous dependency mapping and stronger supplier
disclosures
- Governance must
integrate model risk, cybersecurity, TPRM and operational resilience
- Existing frameworks
remain relevant but require event-driven monitoring and continuous
assurance
- AI concentration
risks could become comparable to systemic cloud dependencies
- Tested alternatives,
fallback arrangements and scenario testing are essential
Log in to continue or register for free
WHAT'S INCLUDED:
Unlimited access to peer-contribution articles and insights
Global research and market intelligence reports
Discover Connect Magazine, a monthly publication
Panel discussion and presentation recordings
Sign in to view comments
Related insights —