
Hidden Vendor Dependencies Are Creating New Compliance Risks for Businesses
- Explores hidden compliance risks within third-party and fourth-party relationships.
- Examines how organizations can simplify oversight while meeting evolving regulatory expectations.
- Discusses the characteristics of resilient and proactive third-party risk programs.
- Highlights emerging risks from AI, digital ecosystems, and supplier concentration.
- Shares insights into the future of compliance and third-party risk management.
- Reviews key capabilities organizations should invest in to strengthen resilience.
display-middle-ads-here
1. Many organizations have established compliance frameworks, yet third parties continue to introduce unexpected risks. What are some of the hidden compliance vulnerabilities you see organizations overlooking most often in their vendor relationships?
One of the most common blind spots is the
assumption that completing due diligence equates to managing risk.
Organizations often have mature assessment processes, but they don't always
have visibility into whether those controls are actually effective when a disruption
occurs.
Another area that's frequently overlooked is
fourth-party dependency risk. Many organizations understand their direct vendor
relationships but have limited visibility into the service providers, cloud
platforms, subcontractors, and technology partners that sit behind those third
parties. When a disruption occurs, those hidden dependencies often become the
source of the greatest operational impact.
I also see organizations underestimating
concentration risk. They may believe they have diversified vendors, only to
discover that multiple critical providers rely on the same cloud
infrastructure, geographic location, telecommunications provider, or specialized
workforce.
Finally, many compliance programs focus
heavily on policy adherence and contractual requirements but don't adequately
measure resilience outcomes. The question regulators and boards increasingly
care about is not simply, "Did you assess the vendor?" but rather,
"Can your organization continue delivering critical services if that
vendor experiences a disruption?"
2. As regulatory expectations continue to
evolve, how can organizations ensure their third-party oversight programs
remain effective without creating excessive complexity or burden for the
business?
The key is to focus on risk-based oversight
instead of attempting to apply the same level of scrutiny to every third-party
relationship.
The most effective programs start by
identifying which vendors truly support critical business services and align
oversight activities accordingly. Organizations can reduce complexity by
concentrating resources on the vendors and dependencies that have the greatest
potential operational, regulatory, or customer impact.
I also encourage organizations to shift from
collecting more data to collecting better data. Too often teams build
increasingly complex reporting structures that generate activity metrics but
offer limited decision-making value. A smaller set of meaningful metrics tied
to readiness, response capability, and recovery performance is often far more
effective.
Ultimately, successful programs create
transparency without overwhelming stakeholders. Executives need concise,
actionable insights, while operational teams need detailed information to
manage risk. Tailoring reporting to those audiences helps organizations remain
effective while avoiding unnecessary administrative burden.
3. What distinguishes organizations that
proactively manage third-party compliance risks from those that tend to react
only when an issue emerges?
The biggest difference is mindset.
Reactive organizations often view third-party
risk management as a compliance exercise. Their focus is on meeting regulatory
requirements, completing assessments, and documenting controls.
Proactive organizations view third-party risk
management as a business resilience discipline. They continuously evaluate how
third-party relationships affect their ability to deliver products and
services, maintain customer confidence, and recover from disruptions.
These organizations typically have three
characteristics in common:
First, they maintain ongoing visibility into
critical third-party relationships rather than relying solely on annual
reviews.
Second, they use operational resilience
metrics to monitor preparedness, response effectiveness, and recovery
performance.
Third, they regularly test assumptions. They
don't simply collect business continuity plans or recovery commitments. They
validate whether those plans work under realistic conditions.
Organizations that prioritize testing,
measurement, and continuous monitoring are generally much better positioned
when disruption occurs.
4. Looking ahead, what new compliance risks
do you believe organizations will need to pay closer attention to as
third-party ecosystems become more digital, interconnected, and AI-enabled?
Artificial intelligence is certainly one of
the most significant areas to watch. Many organizations are now consuming AI
capabilities through third-party providers, often without fully understanding
the models, training data, governance structure, or downstream dependencies
involved. This creates emerging concerns related to transparency,
accountability, model risk, privacy, intellectual property, and regulatory
compliance.
I also believe organizations will need to
become much more sophisticated in understanding systemic risk. As ecosystems
become increasingly interconnected, a single technology provider, cloud
platform, software component, or data supplier can affect thousands of
organizations simultaneously.
Cybersecurity remains a critical concern as
well. The increasing interconnectivity between organizations and third parties
expands the potential attack surface and creates additional pathways for
operational disruption. Going forward, organizations will need stronger
visibility into digital supply chains, AI governance frameworks, and
concentration risks that may not be immediately apparent through traditional
vendor management approaches.
5. How do you see third-party compliance
programs evolving over the next three to five years, and what capabilities
should organizations be investing in today to stay ahead?
I believe we're going to see a significant
shift from assessment-focused programs to intelligence-driven and
resilience-focused programs.
Historically, many TPRM functions have
concentrated on onboarding reviews and periodic assessments. Over the next
several years, I expect organizations to increase investments in continuous
monitoring, operational resilience measurement, automation, and predictive
analytics.
The most mature programs will likely integrate risk, resilience, cybersecurity, compliance, and business continuity data into a more holistic view of third-party performance.
Organizations should be investing today in
three areas:
First, data and analytics capabilities.
Better data enables better decision-making and more meaningful risk
measurements.
Second, operational resilience programs.
Organizations need clear measures of readiness, response capability, and
recovery performance.
Third, dependency mapping and ecosystem
visibility. Understanding critical supplier relationships, fourth-party
dependencies, and concentration risks will become increasingly important as
regulatory expectations continue to evolve.
The organizations that can effectively
connect compliance activities to business outcomes will be best positioned for
the future.
6. What is the one key takeaway attendees can expect from
your session, and why is understanding hidden compliance risks within
third-party relationships more important now than ever before?
The one takeaway I hope attendees leave with
is this: Effective third-party risk management is no longer about proving
compliance. It's about demonstrating resilience.
Organizations are operating in an environment where third-party disruptions can quickly become customer, operational, financial, and reputational events. Boards, regulators, and executive leadership increasingly want evidence that critical services can withstand disruption and recover effectively when challenges occur.
During the session, I'll share practical
examples of operational resilience metrics that organizations are using to
measure readiness, response capability, and recovery performance, along with
approaches for communicating those metrics to both executives and operational
teams.
Understanding hidden compliance risks is more important than ever because many of today's most significant vulnerabilities exist beyond traditional vendor assessments. The organizations that can identify those hidden dependencies, measure resilience effectively, and translate risk information into actionable business insights will be significantly better prepared for the disruptions of tomorrow.
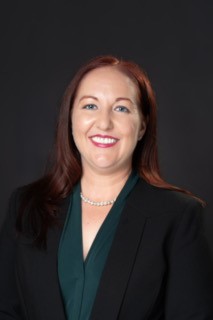
Director, Vigilant LLC
Laura joined Vigilant Compliance, LLC in 2024 as a Director providing regulatory compliance consulting and outsourced CCO services to investment advisers. Prior to Vigilant, Laura was the Information Risk Management Strategist at Barrow Hanley Global Investors, supervising the TPRM and risk management functions for multiple departments and providing executive advisory services and strategic planning across Compliance and IT. Laura is a member of the CFA Institute and the CFA Society of Dallas-Fort Worth. She also holds the Certificate in Investment Performance Measurement (CIPM) certification, the Investment Adviser Certified Compliance Professional® (IACCP) designation, the Certified Third Party Risk Assessor (CTPRP) certification, the Certified in Risk and Systems Control (CRISC) certification, and the Registered Compliance Professional (RCP) certification.
LinkedIn profile




