
Building Trustworthy AI: Why Data Governance is the Foundation of AI Governance
- Data governance must evolve beyond structured data to encompass unstructured and AI-driven environments.
- Successful AI governance builds on existing privacy, cybersecurity, and risk management frameworks.
- Data provenance, traceability, and accountability are essential throughout the AI lifecycle.
- Agentic AI requires enhanced oversight, access controls, monitoring, and kill-switch capabilities.
- Future competitive advantage will depend on trusted, well-governed AI as much as technological advancement.
- Governance investment should be viewed as a business enabler rather than a compliance expense.
As
organisations accelerate AI adoption, many are discovering that effective AI
governance cannot exist without strong data governance foundations. In this
exclusive Q&A, Sebastian Nordgren, Global Head of Privacy & AI
Governance at MUFG, shares his insights on the evolving relationship between
data governance, AI risk management, agentic AI oversight, and the governance
capabilities organisations will need to remain competitive and compliant in the
years ahead.
1. Why
do organisations still struggle to treat data governance as the foundation of
AI governance?
Even before the rise of generative and
agentic AI, many organisations struggled with accountability structures and
often approached data cataloguing, quality, and lineage as one-off projects
rather than ongoing programmes.
According to Sebastian, one of the most
common barriers is the disconnect between business subject matter experts and
data governance specialists. This separation frequently creates inconsistencies
in terminology, differing expectations around data quality, and incomplete data
mapping efforts.
A further challenge is the expanding scope
of governance itself. Traditional data governance programmes focused largely on
structured data, whereas AI initiatives increasingly rely on unstructured,
high-entropy information. Successfully governing these new data environments
requires broader stakeholder involvement, revised operating models, and greater
leadership commitment to supporting governance capabilities at scale.
2. How
can organisations integrate AI risk into existing governance structures without
slowing innovation?
Sebastian believes the most successful
organisations use AI governance programmes as enablers of innovation rather
than barriers to adoption.
Rather than creating entirely separate
governance structures, leading firms leverage existing risk, privacy,
cybersecurity, and compliance frameworks, extending them where necessary to
address AI-specific considerations. In highly regulated industries such as
financial services, however, dedicated AI policies and standards may be
required to meet regulatory expectations and demonstrate accountability.
Examples include enhancing third-party risk
assessment processes, introducing AI-specific vendor requirements, and updating
contractual provisions to address AI-related liability. Sebastian recommends a
simple governance principle: determine whether an existing control can be
expanded before creating a new process.
3. What
controls should organisations prioritise to ensure data provenance and
accountability?
As AI systems increasingly rely on both
internal and external data sources, Sebastian recommends organisations first
maximise the value of controls they already possess.
Privacy impact assessments, data protection
impact assessments, records management practices, retention policies, and data
movement assessments all provide valuable mechanisms for establishing
provenance and accountability throughout the AI lifecycle.
He also stresses close collaboration with
cybersecurity teams. Capabilities such as data loss prevention, identity
management, and access control become increasingly important as AI systems
operate at greater scale and complexity.
Alongside technical controls, organisations
should implement consistent information classification frameworks across all
data types and utilise recognised benchmarks such as the EU AI Act and the NIST
AI Risk Management Framework to create a common governance language.
4. What
new governance capabilities will be required for agentic AI?
As autonomous AI agents become more capable
of interacting with systems, making decisions, and executing actions,
governance frameworks must evolve accordingly.
Sebastian suggests organisations should
treat AI agents similarly to new employees by applying least-privilege access
principles and carefully evaluating requests for highly privileged access.
Continuous monitoring of agent behaviour, token usage, and risk indicators
should become standard practice, alongside rigorous testing and adjustment of
guardrails.
He also highlights the importance of
thoroughly tested kill-switch mechanisms and formal onboarding processes for
new data sources and APIs. Ultimately, the trustworthiness of any agentic AI
system depends heavily on the quality and governance of the data environment it
can access.
5. Will strong governance become a greater competitive advantage than advanced AI models?
Looking ahead, Sebastian argues that
business value, rather than model sophistication alone, will determine
competitive success.
Drawing parallels with long-established data
quality principles such as "fit-for-use" and
"fit-for-purpose," he notes that AI systems only create value when
their outputs are trusted, explainable, and aligned with human-centric principles.
Data governance serves as a foundational
element of this trust because it enables organisations to demonstrate
accountability rather than simply claim it. Sebastian believes the key
indicator leaders should monitor is whether AI governance investment is viewed
solely as a compliance obligation or as a prerequisite for sustainable scale
and growth.
Over the next several years, organisations
that underinvest in governance may encounter similar challenges to those that
fail to invest in AI innovation itself, placing them at a significant
competitive disadvantage.
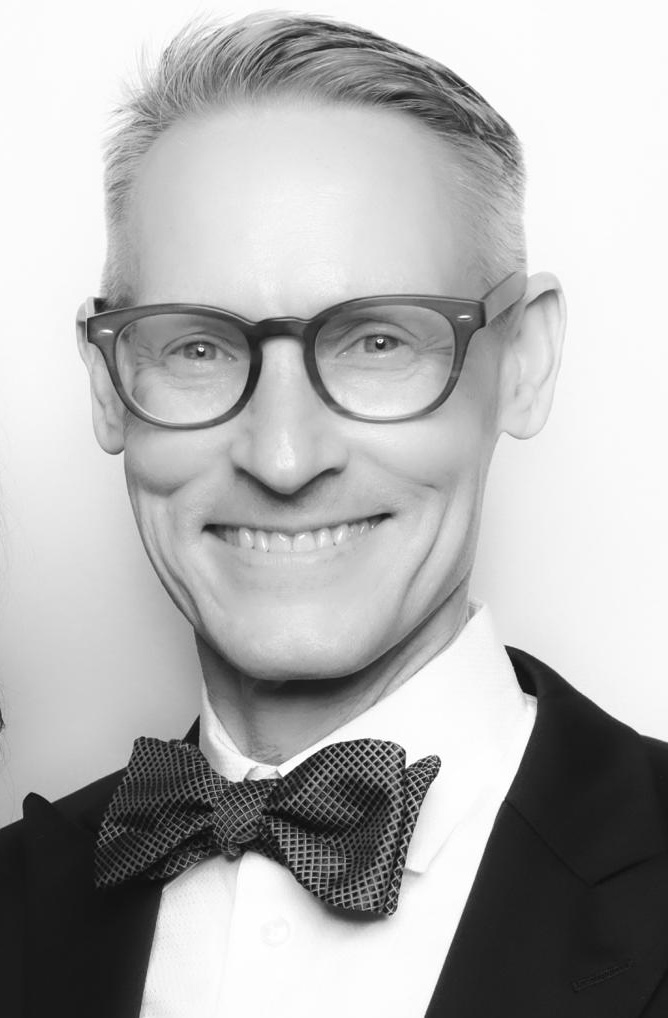
Former Global Head of Privacy & AI Governance, Director, MUFG Bank
Sebastian Nordgrén has spent over 20 years in financial services in New York across technical, risk, and leadership roles. An original contributor to the Business Intelligence, Data Privacy, and AI Governance domains, he first joined MUFG in 2004, helping develop the industry's first data management maturity model with the IBM Data Governance Council, returning in 2019 as the Global Head of Data Privacy Governance and launching MUFG's AI Governance program in 2023. Sebastian has led major regulatory transformations at Citigroup and co-chaired the U.S. Treasury's BSAAG Information Security and Confidentiality subcommittee. He holds an M.Sc. from KTH in Stockholm Sweden.





